On this page
"Zero-knowledge" is on a lot of password manager landing pages. It is a useful phrase and a slippery one. Here is the specific claim we make for PulsVault, and the things it does not cover.
Short answer: zero-knowledge, for a password vault, means the server only ever stores ciphertext, because the key is derived from your master password and used on your device. It does not hide account metadata, protect a compromised device or let anyone recover a lost master password.
The claim
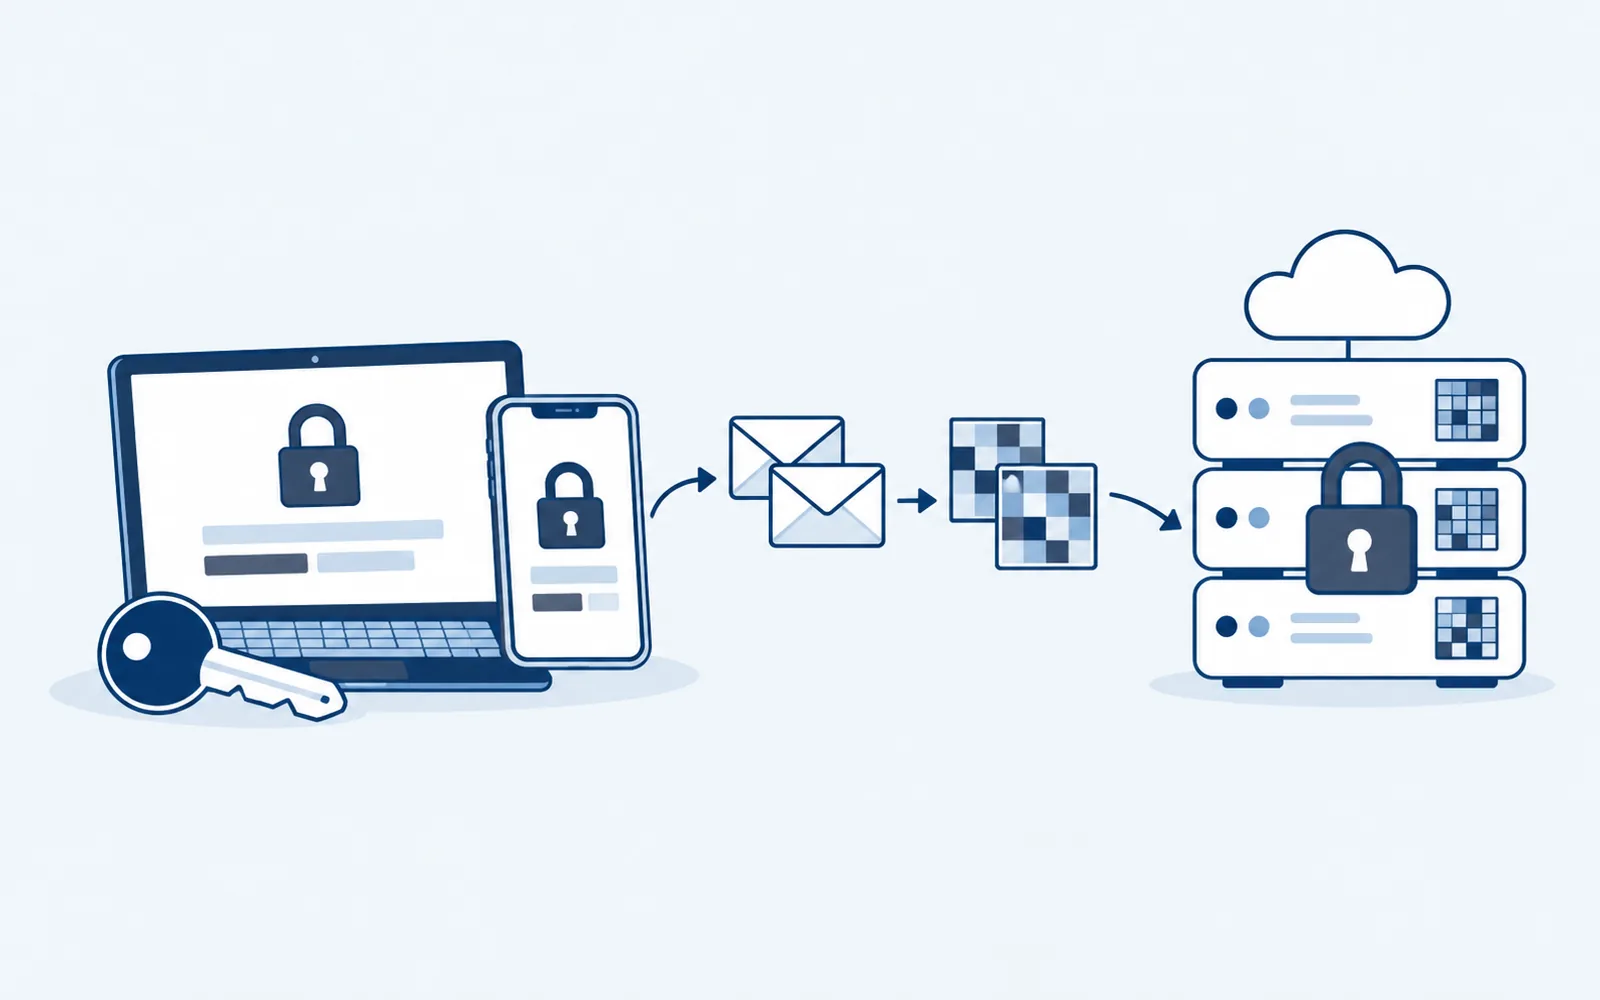
The server never has what it needs to read your vault. Encryption and decryption happen on your device, with a key derived from your master password. What we store is ciphertext, plus the metadata needed to sync it.
How the key is derived
Your master password is never sent anywhere. The client stretches it into a key using a deliberately slow key-derivation function, then uses that key to encrypt each item. The sketch below uses PBKDF2 with 600,000 iterations, the OWASP-recommended setting for PBKDF2-HMAC-SHA256 and the option built into the Web Crypto API. Memory-hard functions such as Argon2id (RFC 9106) make offline guessing costlier still.
const salt = crypto.getRandomValues(new Uint8Array(16));
const baseKey = await crypto.subtle.importKey(
  "raw",
  new TextEncoder().encode(masterPassword),
  "PBKDF2",
  false,
  ["deriveKey"],
);
const vaultKey = await crypto.subtle.deriveKey(
  { name: "PBKDF2", salt, iterations: 600_000, hash: "SHA-256" },
  baseKey,
  { name: "AES-GCM", length: 256 },
  false,
  ["encrypt", "decrypt"],
);
This is a simplified sketch of the shape, not our production code. The point is that vaultKey exists only in the browser or app, and is created as non-extractable.
What zero-knowledge does not mean
It does not hide metadata
We can see that an account exists, how many items it holds, when it last synced and how large the encrypted blobs are. We do not see titles, URLs, usernames or passwords.
It does not protect a compromised device
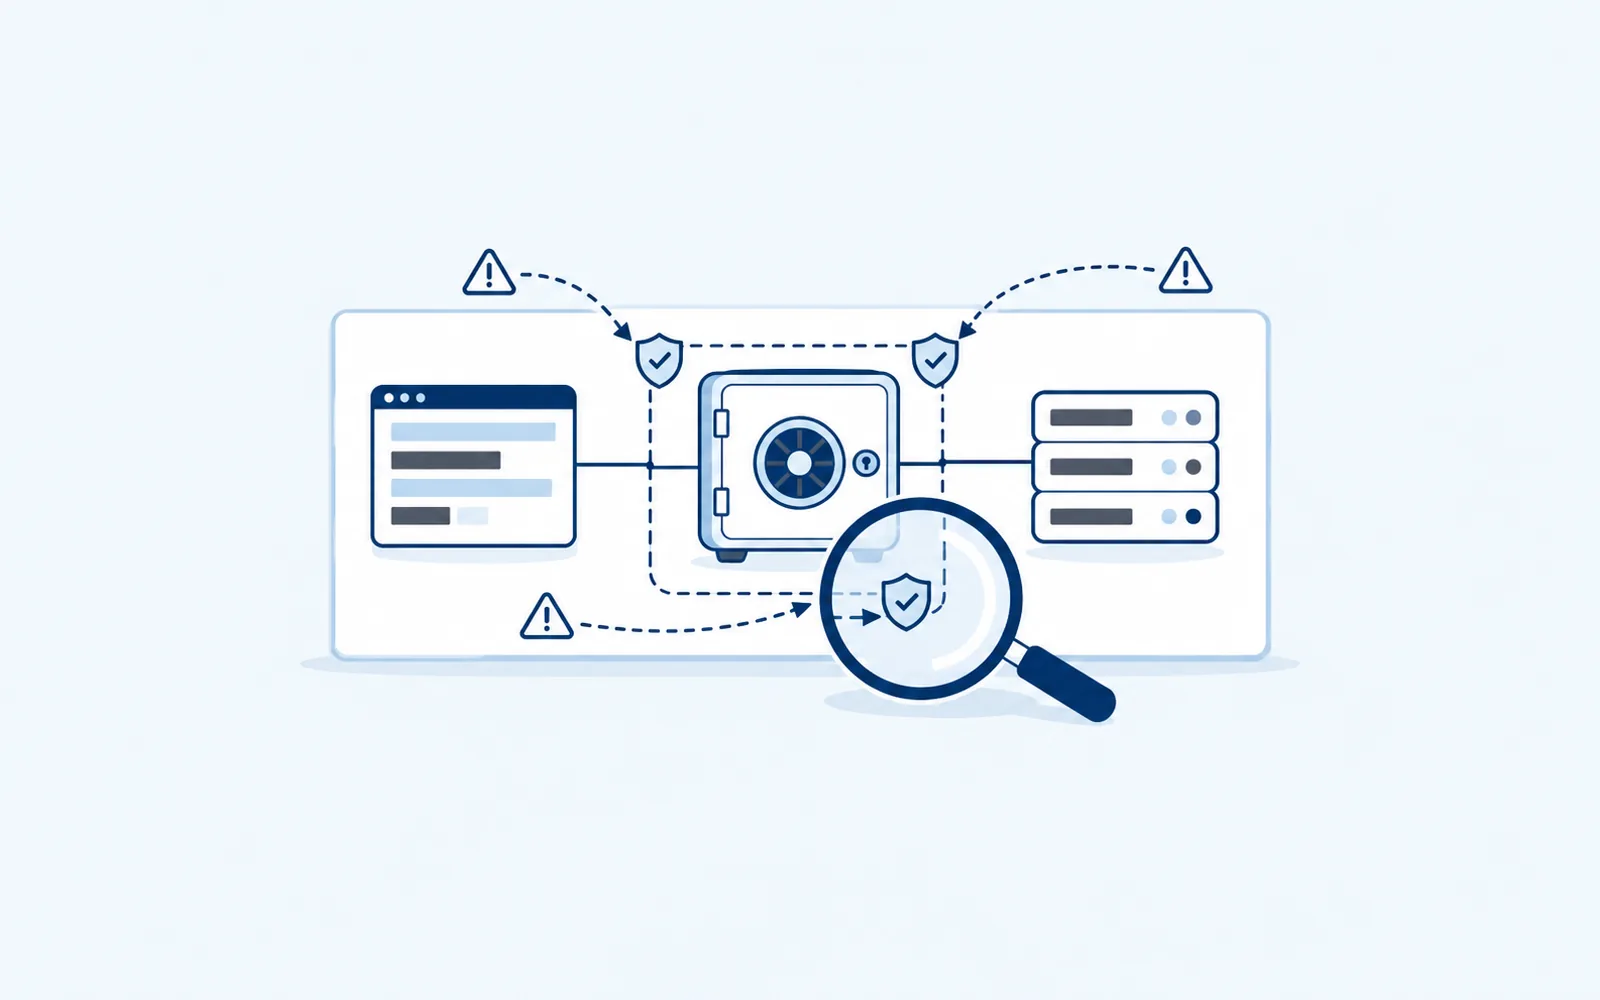
If malware can read your screen or memory while the vault is unlocked, no server design helps. Zero-knowledge limits what we can leak. It does not make your laptop safe.
It does not recover a lost master password
This is the trade-off people feel most. If we cannot read your vault, we cannot reset your password into it. PulsVault offers a recovery code you store yourself. Lose both and the data is gone, by design.
How you can check us
A claim you cannot verify is marketing. We publish the encryption format, and the client code that performs it runs in your browser, where you can inspect the network traffic and confirm that no plaintext leaves the device. The same verify-it-yourself principle shapes our security and compliance work for clients.
Questions to ask any vendor
- Where is the key derived, and can the server ever see it?
- What exactly is in the sync payload besides ciphertext?
- What happens to my data if I forget my master password?
If the answers are vague, the phrase is doing the work that the design should be doing.
Found this useful? Share it with your team.
Share on LinkedInRelated product
PulsVault
Security
Zero-knowledge credential vault. Your secrets are encrypted before they ever leave your device.