Cloud & security
Security & compliance engineering to close the enterprise deal.
Enterprise buyers send security questionnaires before they sign. We build the controls they ask for into your product, and produce the technical evidence your auditors and customers need, from UK GDPR to ISO 27001, SOC 2 and the EU AI Act.
- Security & compliance engineering
- 3–10 weeks
When to call us
Sound familiar?
- 01
A large customer sent a security questionnaire you cannot fully answer.
- 02
A penetration test came back with findings you need fixed quickly.
- 03
Your product uses AI for hiring, credit or other high-risk decisions in the EU.
How Tulmira handles it
Our approach, step by step
- 1
Gap assessment
We map your product against the framework or questionnaire you face and list exactly what is missing.
- 2
Threat model
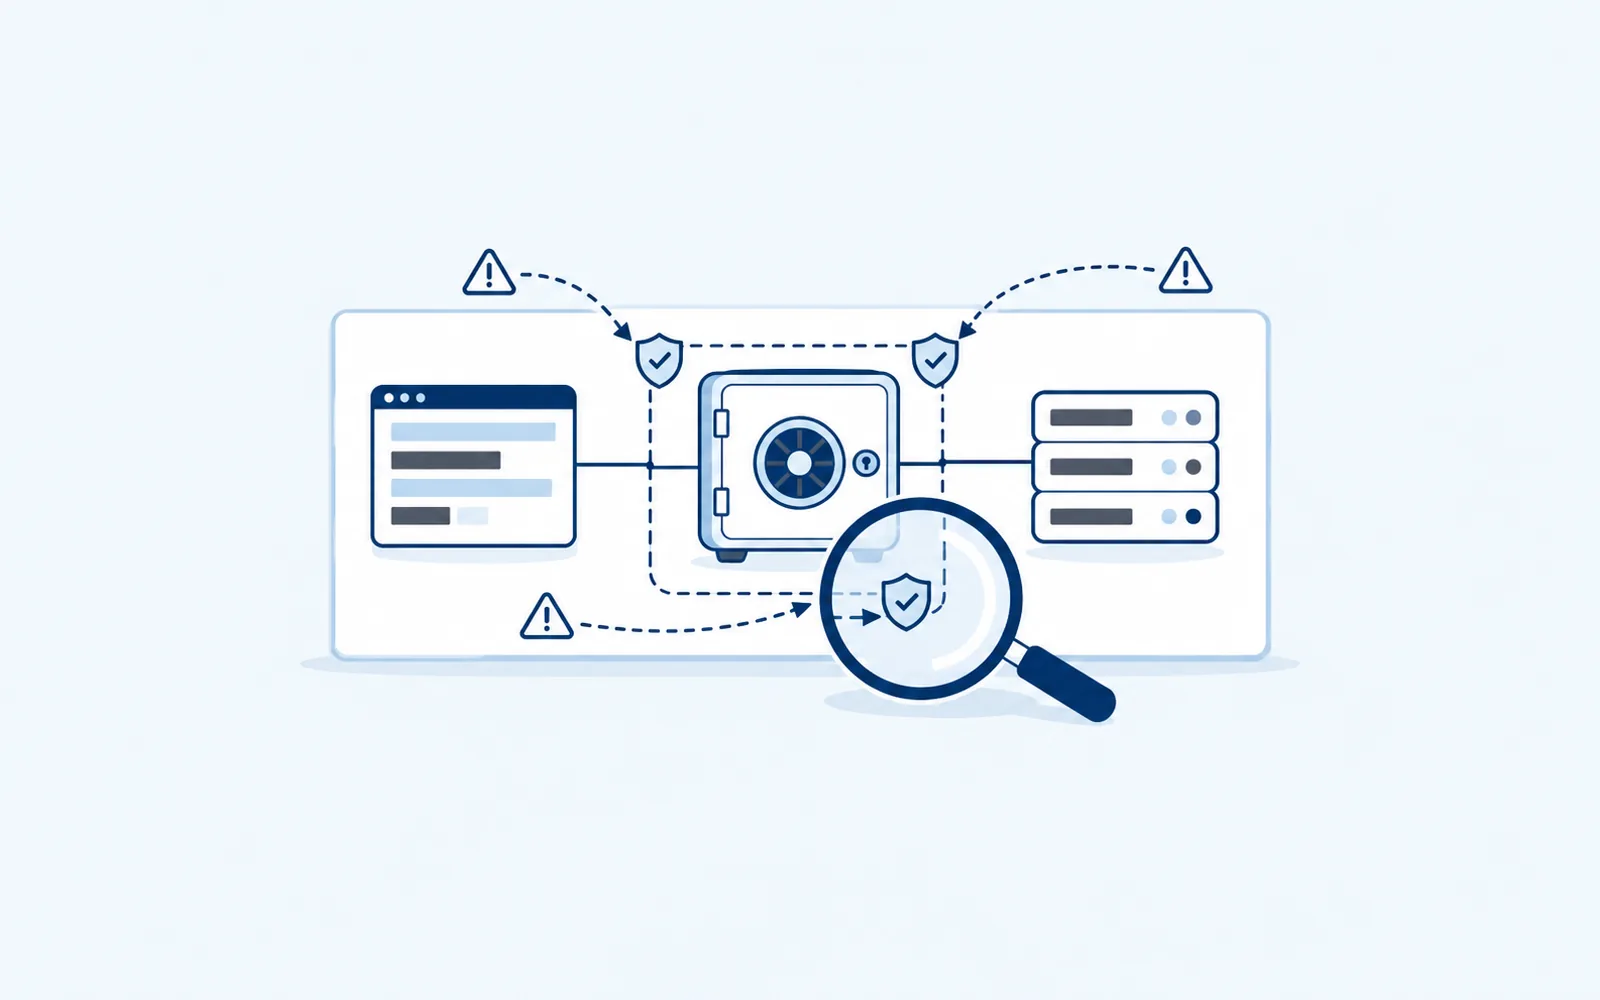
A written threat model of your system, so effort goes where real attackers would.
- 3
Build the controls
SSO and SCIM, role-based access, audit logs, encryption, secrets management and secure pipelines.
- 4
Evidence and handover
Policies, diagrams and automated evidence collection, ready for auditors and customer reviews.
Our standards
Non-negotiable practices
- Threat modeling before security work starts
- Encryption in transit and at rest by default
- Audit logs that record who did what, and when
- Dependency and container scanning on every build
- Data protection impact assessments for personal data
- AI systems documented for EU AI Act risk classification
What you get
- Gap assessment and prioritized remediation plan
- Enterprise security features: SSO, SCIM, roles and audit logs
- Remediated penetration-test findings
- Technical documentation and evidence for audits
Tools we use for this
- OAuth 2.1
- SAML
- OpenID Connect
- Vault
- Snyk
- AWS KMS
Proof
Built the same way we build our own products
PulsVault
Security
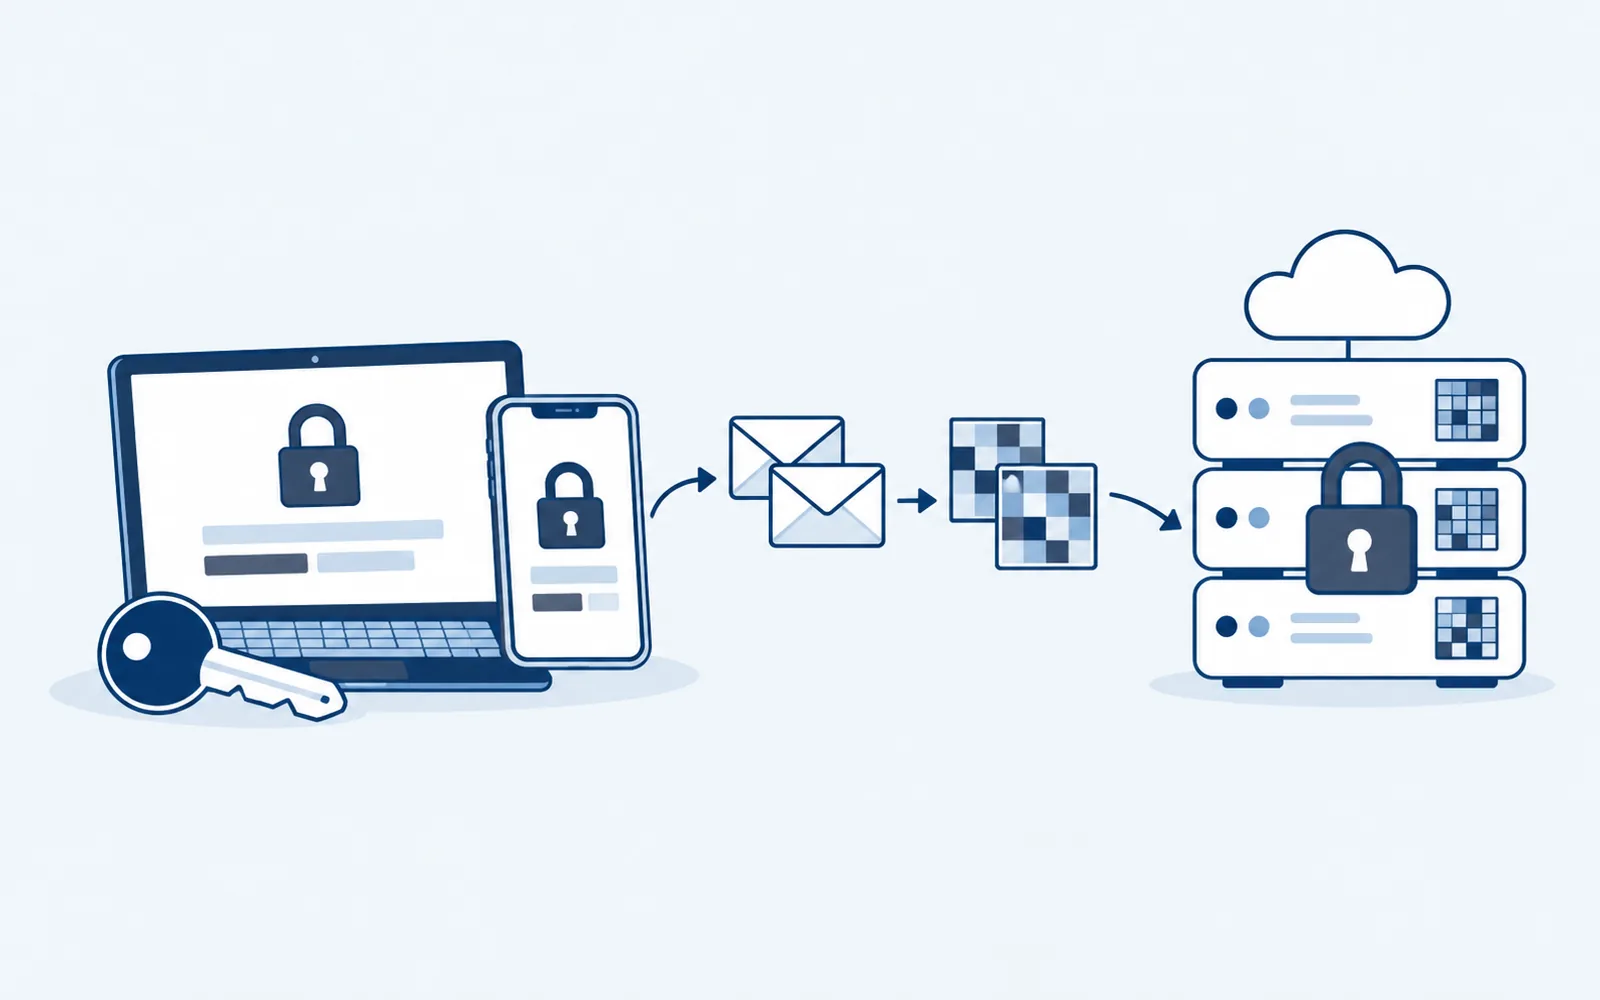
PulsVault's zero-knowledge encryption and published threat model show how we approach security by design.
See PulsVault →Keep reading
Certification is granted by independent auditors. We build the technical controls and evidence they assess, and work alongside your compliance partner.
If you place AI systems on the EU market, possibly. Uses such as hiring and credit scoring are classed as high-risk, with obligations on logging, human oversight and documentation. We assess your use case and build the logging, oversight and documentation it requires.
We prepare for them and fix the findings. The test itself should be done by an independent, accredited tester, which we can help you choose.
Yes. We work through it with you, answer what your product already does, and turn the gaps into a prioritized plan, so the next questionnaire takes hours rather than weeks.
We add SAML and OpenID Connect, so customers sign in through their own identity provider, such as Microsoft Entra ID, Okta or Google Workspace, plus SCIM so their admins can add and remove users automatically.
If you serve people in both the UK and the EU, usually yes. The two are closely aligned, so one set of technical controls, such as data minimization, access control, encryption and records of processing, generally covers both. Your legal adviser confirms the obligations; we build the controls.
Related services
Cloud & platform engineering
Pipelines, infrastructure as code and Kubernetes set up so your team can deploy on a Friday without fear.
- CI/CD
- Kubernetes
- Terraform
AI integration
LLM features that earn their place: retrieval, structured extraction and scoring with evaluation built in.
- LLMs
- RAG
- Evaluation
AI agents & MCP servers
Agents that act on your systems safely: MCP servers for your data and tools, OAuth, guardrails, human approval and full audit logs.
- Agents
- MCP
- Guardrails
One email a month. Only new posts.
No tracking pixels, no promotions. Unsubscribe in one click.
Ready to talk about Security & compliance engineering?
Projects typically start from a scoped proposal. We reply within 2 business days.
Start a project